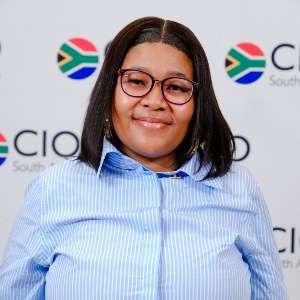


Galeboe Mogotsi, industry leader and cybersecurity expert at the University of the Witwatersrand, shares the importance of creating a culture of security awareness.
In recognition of Cybersecurity Awareness Month, CIO South Africa spoke with Wits University’s award-winning CISO Galeboe Mogotsi to discuss the critical role of human behaviour in organisational security and the need to move beyond compliance-driven approaches. He shares insights on how leadership, culture and continuous engagement can strengthen security awareness across all levels of an organisation.
Q: How do you define human and behavioural risk in the context of cybersecurity within modern organisations?
A: Human and behavioural risk is the potential for individuals’ actions, whether intentional or unintentional, to compromise security. This includes everything from weak password practices, falling for phishing attempts, mishandling sensitive information, to insider threats. In today’s digital-first organisations, the human element often represents both the strongest defence and the weakest link.
Q: What strategies have you found most effective in creating a culture of security awareness that goes beyond compliance training?
A: A compliance-first mindset reduces cybersecurity to a checklist exercise. To go beyond this, I focus on embedding cybersecurity into the organisational culture. Storytelling, simulations and scenario-based learning resonate more than static training.
For example, phishing simulations tied to real-life cases create relatable learning moments. Recognition and positive reinforcement like rewarding secure behaviour makes security feel like part of everyday work rather than a burden, which also helps with building a culture of security.
Q: How can CISOs better engage employees at all levels to take ownership of security behaviours rather than relying solely on technology?
A: Ownership comes from empowerment. CISOs should communicate that security is not just an IT responsibility but a shared accountability. By making security relevant to employees’ personal and professional lives by, for instance, teaching them how the same practices that protect their work data also safeguard their families online, we bridge the gap. Open communication channels, where employees can report suspicious activity without fear of blame, also foster engagement.
Q: What role does leadership play in modelling the right behaviours and reducing human-related security risks?
A: Leadership is critical in setting the tone. When leaders consistently demonstrate secure behaviours, such as using MFA, being cautious with emails or adhering to data protection policies, they send a strong message that cybersecurity is a business priority. Leaders who visibly prioritise security create a ripple effect across the organisation, shifting security from being “IT’s problem” to being part of how the organisation does business.
Q: How can organisations measure the impact of behavioural interventions and awareness programmes on reducing risk?
A: Measurement requires moving beyond attendance sheets. Organisations can assess impact through metrics such as phishing click rates, reporting rates of suspicious emails, incident response times and employee feedback surveys. Longitudinal tracking of these metrics provides insight into whether awareness translates into behaviour change. When aligned with incident trends, these metrics become powerful indicators of programme effectiveness.
Q: What are the most common misconceptions business leaders have about human and behavioural risk, and how do you address them?
A: A common misconception is that technology alone can solve cybersecurity challenges. While firewalls, AI-driven monitoring and endpoint protection are vital, they cannot fully protect against human error or malicious intent. Another misconception is viewing training as a once-off exercise. I address these by emphasising that cybersecurity is 80 percent people and processes and only 20 percent technology. Regular communication with leadership, backed by real-world breach examples, helps reinforce this message.