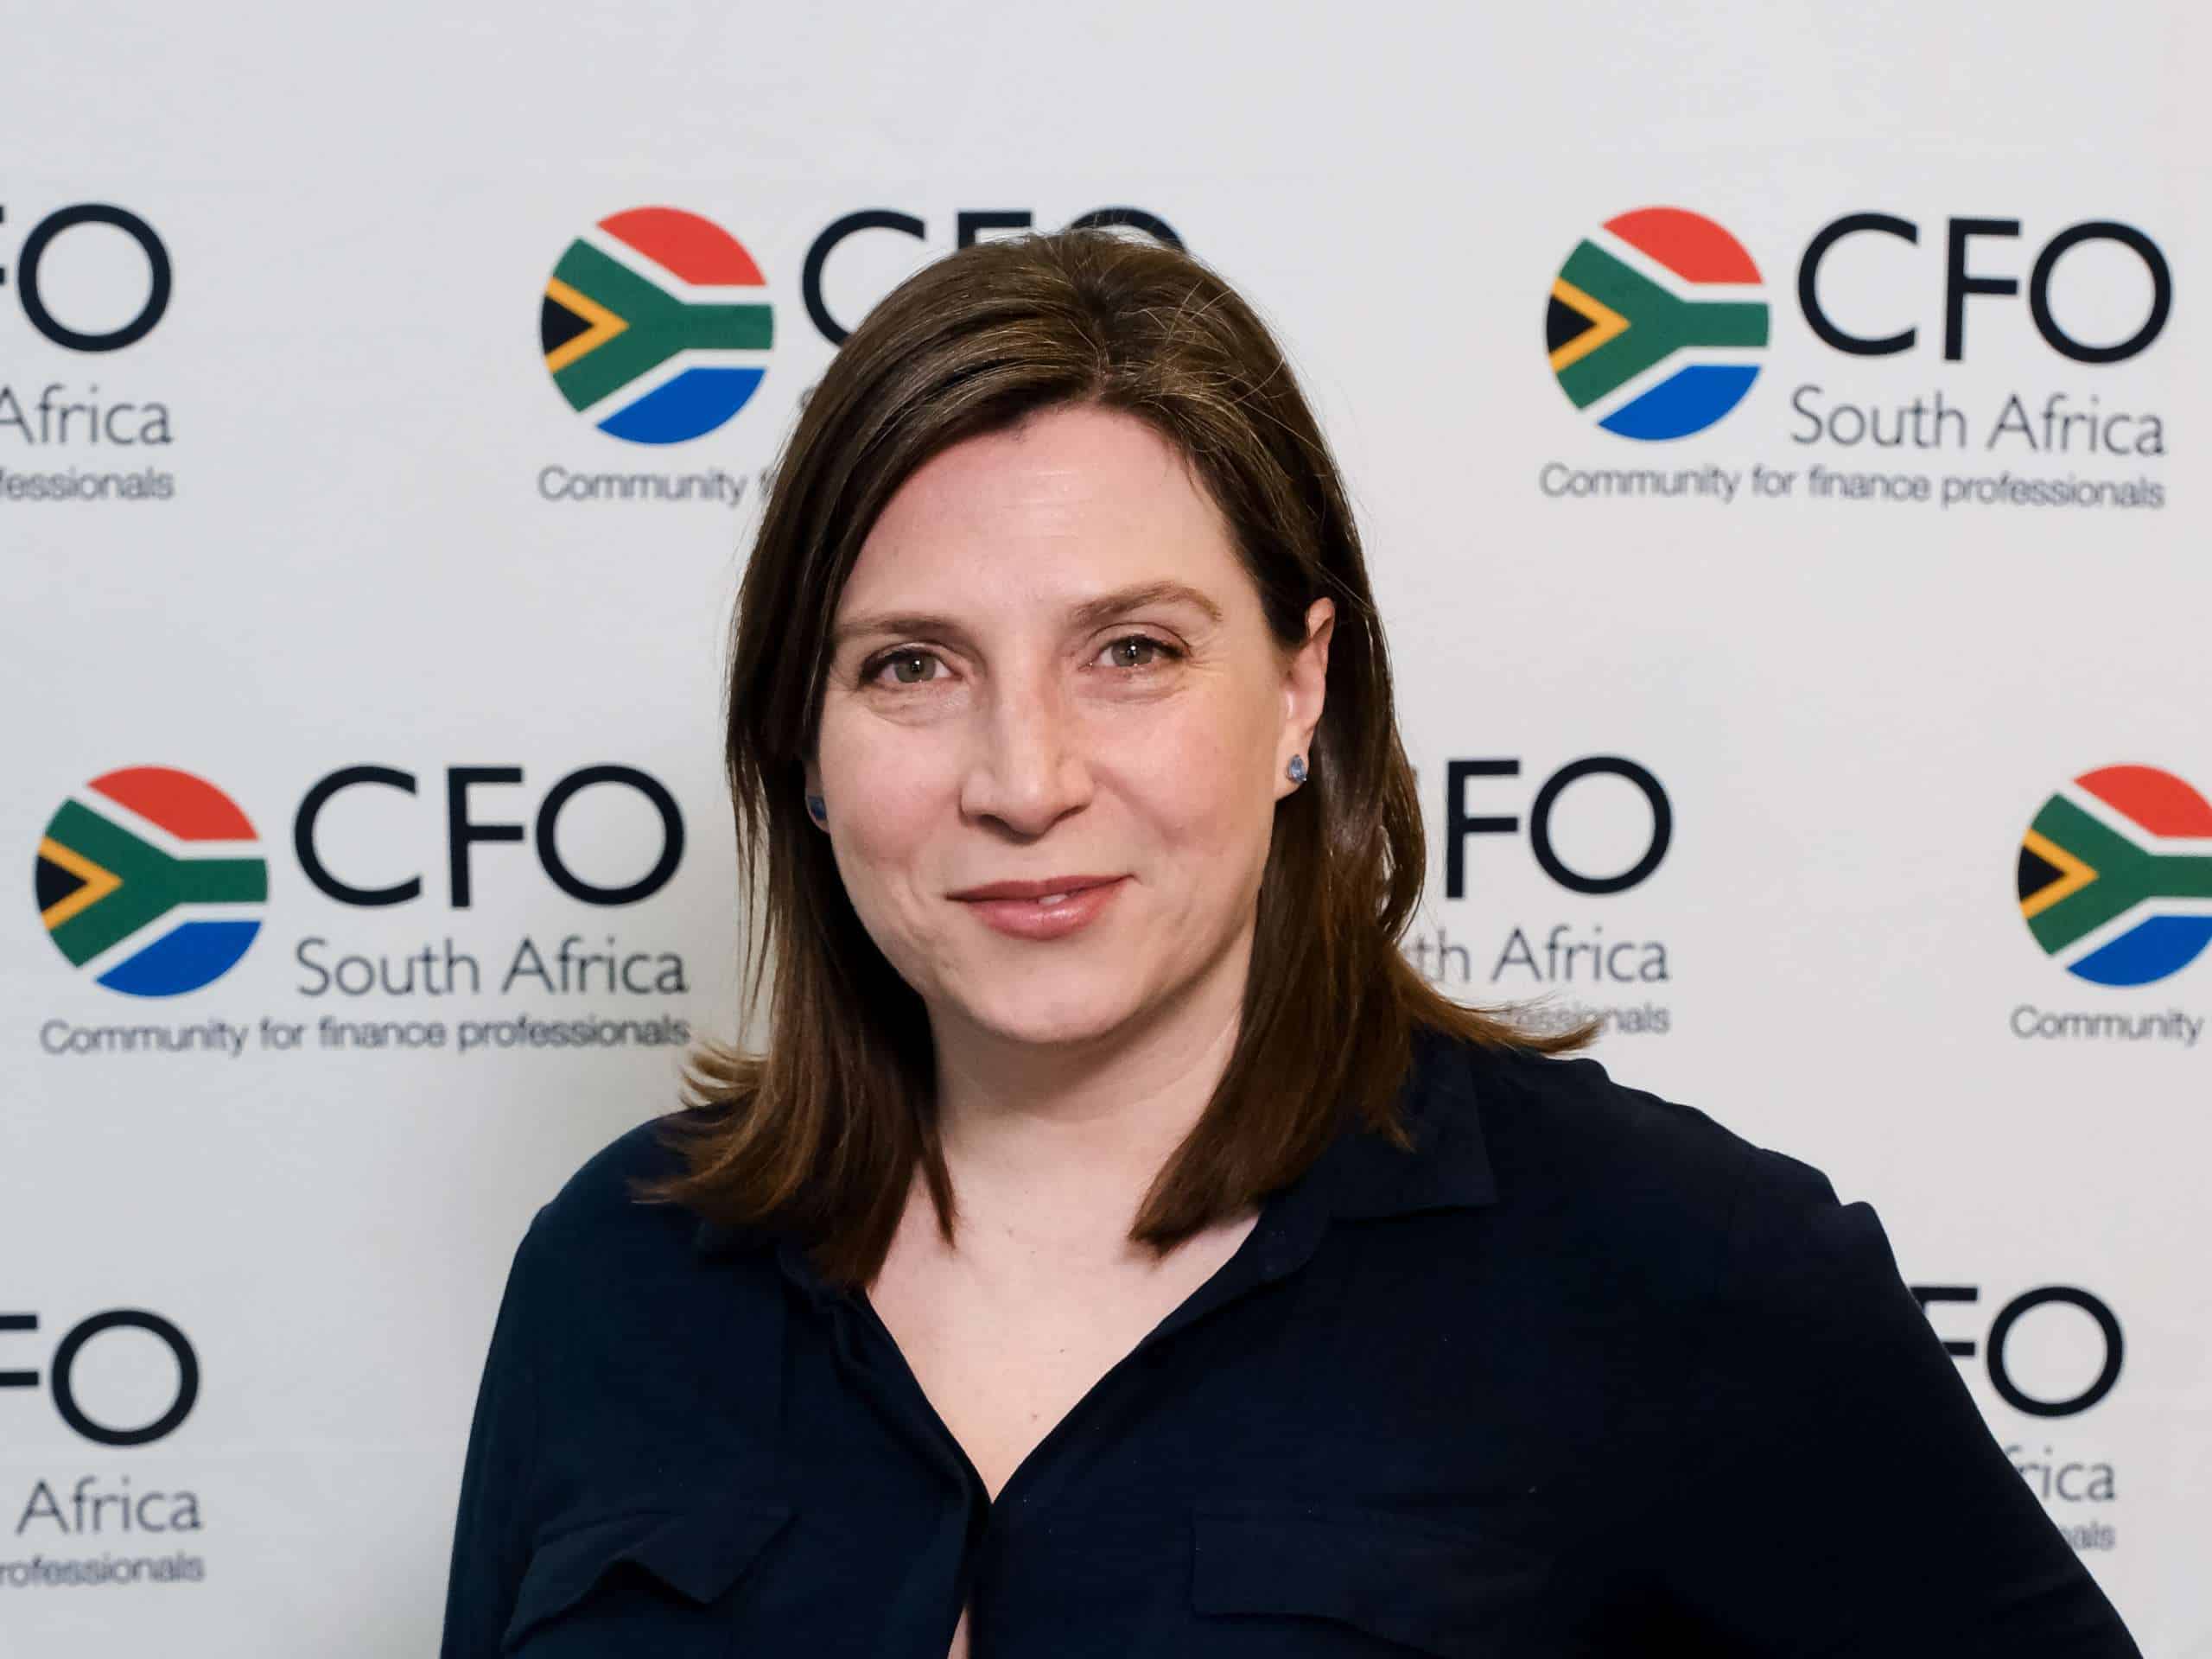


Assess data security levels, test vulnerabilities, ask vendors for security protocols, says EasyBiz’s Gary Epstein.
With the Protection of Personal Information Act (POPIA) coming into effect, it is critical for organisations that have access to their clients’ sensitive information to be aware that they are prime targets for cyberattacks.
Under the act, businesses have been given more responsibility to use data ethically, compliantly and securely. The goal of the POPIA is to ensure the lawful processing of personal information.
The intentions of the Act are two-fold:
- Facilitate everyone's right to privacy as enshrined in South Africa’s constitution, and
- From an economic standpoint, ensure that adequate internationally-recognised data protection legislation is in place for when South African entities trade with international partners.
The likelihood of cyber threats has increased across the world as businesses migrate to online platforms and embrace digital advancement to improve productivity.
Most cyberattacks are aimed at extracting money – these are ransomware attacks, which would be of particular concern to accountants who handle other people’s money. “A data breach is expensive and can result in substantial financial losses,” says Gary Epstein, managing director of EasyBiz Technologies. “In addition, you could lose clients and struggle to get new ones as clients lose trust after such an event.”
Assessing data security levels and testing the vulnerabilities are necessary to ensure adequate protection. “Just as important is that your company’s software protects you from cyberattacks. Make sure that you ask the vendor for their software security protocols,” says Gary.
What is needed is advanced, industry-recognised security safeguards to keep financial data private and protected, with password-protected login, multi-factor authentication, firewall-protected servers and state-of-the-art encryption technology for data at rest and in transit.
Data protection of personal information is also essential. It is concerned with the processing of personal data, which carries particular risks in terms of how it is collected, stored and disseminated. Personal data can reveal who a person is, their financial details, and more. Its processing can therefore pose serious risks to a person’s basic rights.
Data back-up is another crucial consideration. Software should have automatic offset storage so there is no need to create physical backup copies. Should a computer be hacked, all of the data must still be accessible from any computer connected to the Internet.
Hacking methods are continually evolving as fraudsters find new ways to execute attacks.
“You need to have software that protects your business, and every employee must be aware of the threat and follow protocols outlined by the software provider and your IT team,” says Gary.
“You can promote awareness about cybersecurity and best practices among your employees, hire a security architect, strategise a response plan, and leverage the cloud for better data security,” he adds.